Data security and privacy
Join2Data is designed so the client always knows what they share, with whom and how to withdraw it.
What we store and what we don't
What we store
- Name and email of the client and of team members
- The connected Google account and the services and resources it shares
- The tokens Google issues to access those services, encrypted at rest with AES-256-GCM
- A usage log: who queried, which client, which tool and when, without the content of the answers
What we don't do
- We don't store Analytics, Search Console or Tag Manager data: it is queried on the spot, at the request of authorised team members
- We never write to or change anything in Google accounts
- We never ask for Google passwords or see them
- We don't use data for advertising or to train AI models
Access controls
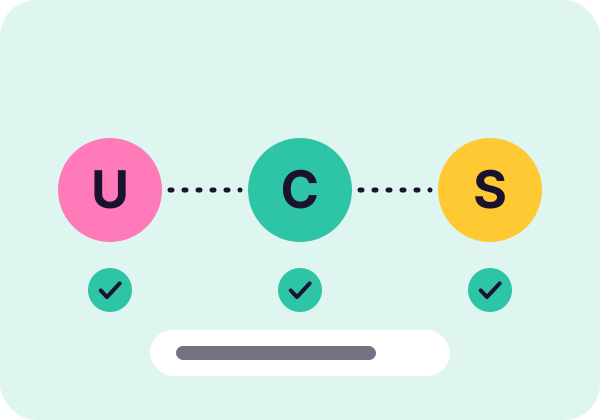
Per client, service and resource
Every call is checked on the server: user, client, service, shared property and current connection.
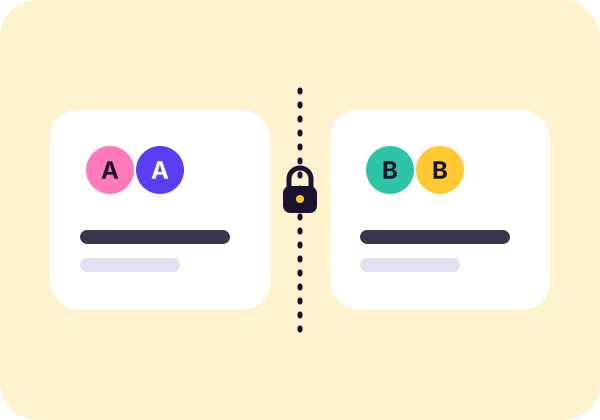
Isolated agencies
Each agency only sees its own clients. The platform administrator has no access to client data.
Links that expire
Sign-up links expire and can be revoked. Our own tokens are stored only as a fingerprint, never in clear.
How to withdraw access
The agency can remove a service or deactivate the client from the dashboard. The client can also revoke access at any time from their Google account permissions. When a client is disconnected or deactivated, the tokens are deleted.
Join2Data complies with the Google API Services User Data Policy, including the Limited Use requirements.